1. Accounts and devices
Protect accounts, verification codes and trusted-device permissions
Do not use JDesk to access devices without authorization or to bypass target-side authorization.
These terms summarize account security, authorized remote access, plan entitlements and service changes. Purchase confirmation and formally published legal notices remain authoritative.
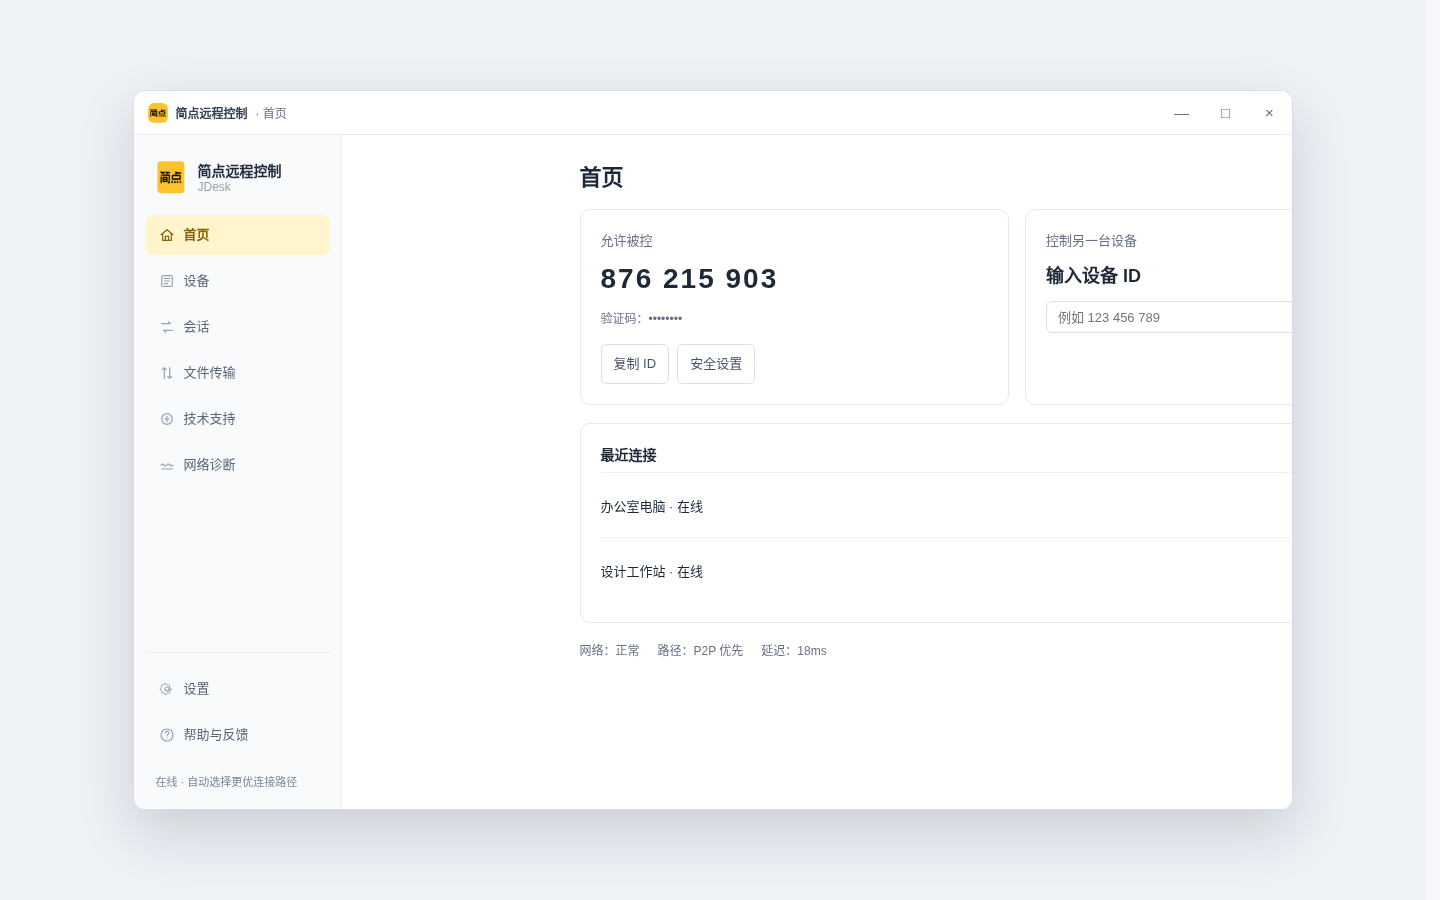
Do not use JDesk to access devices without authorization or to bypass target-side authorization.
Security controls may restrict anomalous connections and abuse.
Security fixes, compatibility changes and material service updates are communicated through the product or official website.
Core remote access remains simple; advanced performance and governance are enabled by published entitlements.